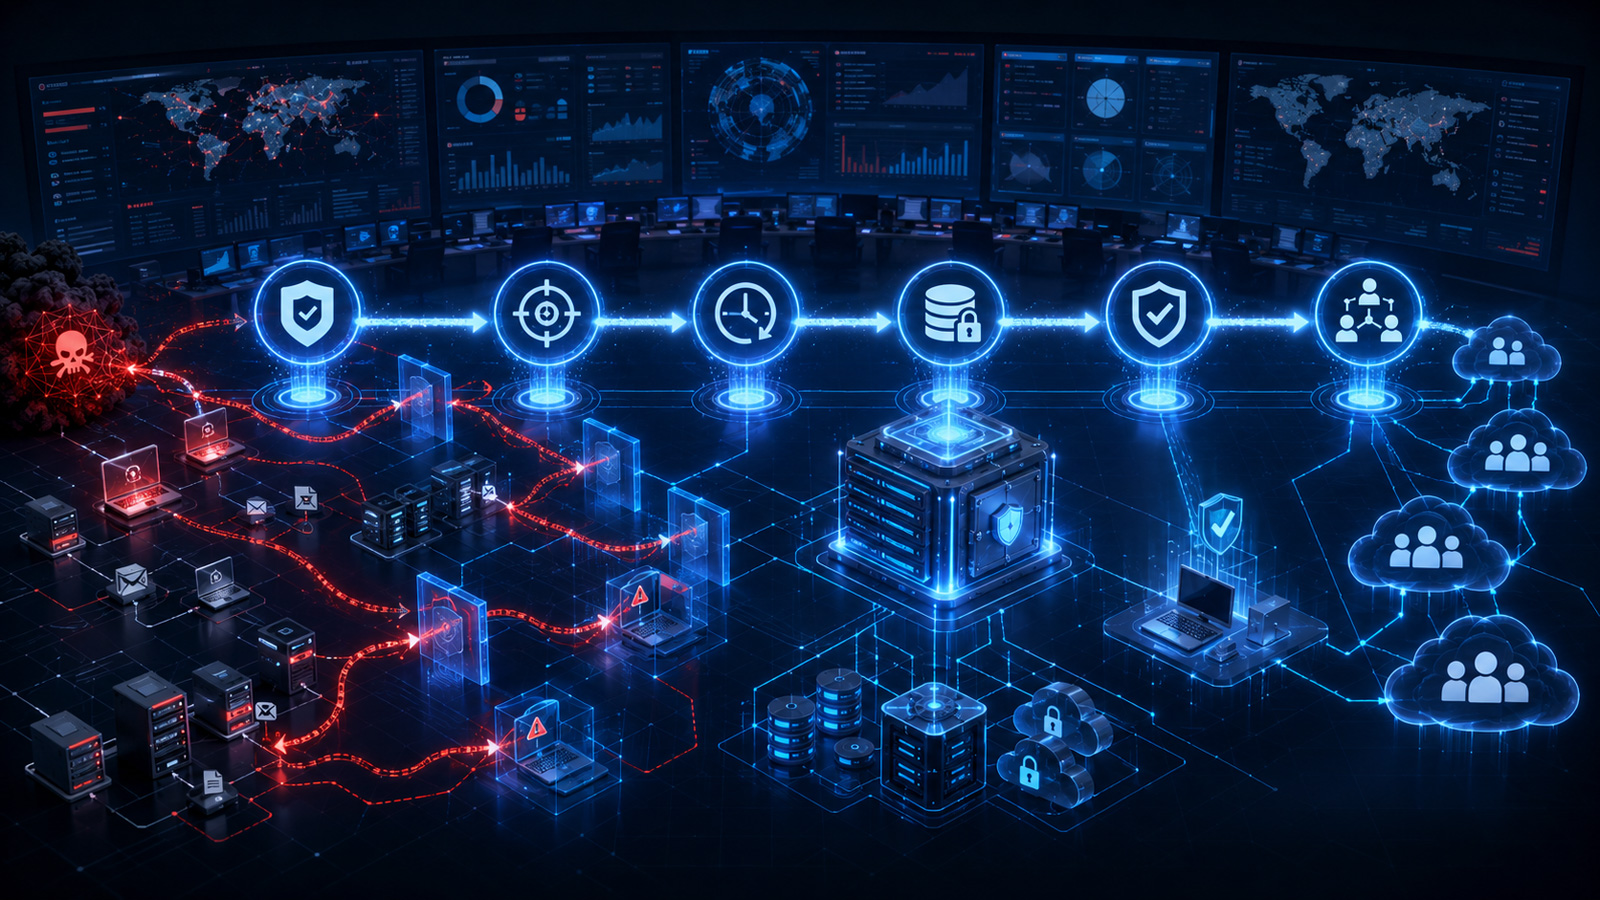
Ransomware protection for MSPs should deliver six tested outcomes: reduce exposure, detect activity before encryption, provide 24/7 response, preserve isolated recovery points, recover cleanly and operate consistently across tenants. Backup alone is not enough, and neither is endpoint detection without a rehearsed recovery path.
The Acronis Cyberthreats Report identified 143 MSP, IT-service provider and telecom ransomware victims in 2025, with phishing accounting for 52% of initial access cases and unpatched vulnerabilities for 27%.
The checklist below turns those failure modes into controls and evidence an MSP should require before calling a service complete.
The six things your service must do and what to verify
A complete ransomware protection service connects prevention, detection, response and recovery. For each control, demand evidence from the exact tenant, workload, storage configuration and service tier being sold.